PatchClock

EU Cyber Resilience Act compliance

Your CRA clock, handled

For PHP software vendors, from Laravel apps to WordPress plugins and Shopware extensions. Know what the Cyber Resilience Act expects, keep your SBOM and support period current, and meet the 24-hour reporting deadline when it matters.

WORKS WITH

Why PatchClock

Small software teams now carry the same legal duties as big vendors. The rules are clear on paper and vague in practice. PatchClock turns them into a short list of things to keep true, checks them for you and tells you when one slips.

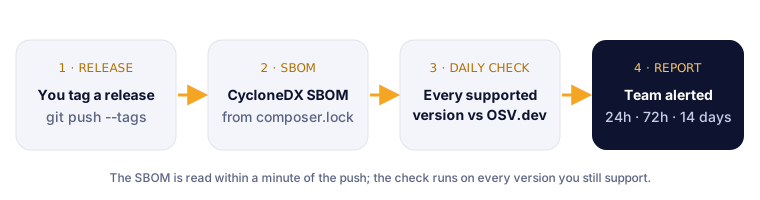
How PatchClock works: you tag a release, PatchClock writes a CycloneDX SBOM from composer.lock, checks every supported version against OSV.dev each day, then alerts your team and opens the 24-hour, 72-hour and 14-day reports.

Find your path

● FREE CRA CHECK

Free CRA readiness check

We read your public pages and, if you add one, a public GitHub repository. You get a report on your security.txt, your disclosure policy, the dependencies you ship and your support period. When we cannot verify something from outside, we say so instead of guessing.

Only public pages and public files are read.

security.txt

Missing at /.well-known/security.txt

Vulnerable dependencies

guzzlehttp/psr7 2.4.3, CVE-2023-29197

SECURITY.md

Disclosure policy with contact
● INCIDENT RUNBOOK

Three deadlines, one screen

When a vulnerability in your product is actively exploited, Article 14 gives you 24 hours for an early warning, 72 hours for the notification and 14 days after the fix for the final report. PatchClock opens the incident, drafts each report from what it already knows and lists who to tell.

Early warning

18:42:07

Notification

66:42:07

Final report

14 days

  • ✓ Draft reports
  • ✓ Affected versions
  • ✓ Customer notice
  • ✓ Evidence log
● ALWAYS CURRENT

SBOM, support period and policy

Every release you tag regenerates a CycloneDX SBOM from composer.lock and package-lock.json, read within a minute of the push. You declare which versions you still patch, and PatchClock publishes it as a page your customers can read, next to a hosted disclosure policy and a hosted security.txt that renews itself, with a warning before the copy on your own site expires.

When an EU customer asks for your SBOM before they sign, you already have it for the version they run.

✓ 128 packages read from composer.lock
✓ sbom.cdx.json updated
✓ v4.x supported until Dec 2031, v3.x until Jun 2028
! security.txt on your site expires in 21 days: team warned

A NOTE FROM THE FOUNDER

João Ribeiro
“Big vendors have compliance departments. Teams of five don't, and they still have to meet the same rules, which is why I'm building PatchClock for them.”

I build PatchClock on my own, from Portugal, as a Laravel app. You write to me, not to a sales team.

João Ribeiro, founder · hello@patchclock.com · Profile · About
● WHY NOW?

The CRA is already here

The EU's Cyber Resilience Act, Regulation (EU) 2024/2847, has required reporting of actively exploited vulnerabilities since 11 September 2026, including for products already on the market.

From 11 December 2027 every essential requirement applies: technical documentation, an SBOM, a declared support period and the EU Declaration of Conformity. Breaches can be fined up to €15 million or 2.5% of worldwide turnover, whichever is higher.

Not sure it covers you? Read does the CRA apply to your PHP or Laravel product.

● FOUNDING MEMBERS · 50 PLACES

Founding member offer: lock in your price

The first 50 vendors keep the founding price for as long as they stay. Access opens on 15 December 2026.

  • Incident runbook with 24h, 72h and 14-day clocks
  • SBOM and CVE alerts for Composer and npm
  • Public support period page
  • Hosted security.txt
  • Customer vulnerability notices
  • Declaration of Conformity template
  • Technical documentation in Annex VII order

Founding price

€190 per year excl. VAT

3 products · 5 people

The same as Studio at €390 a year after launch, for less than half.

  • ✓ Price locked for as long as you stay
  • ✓ Full refund if we miss 15 December 2026
  • ✓ Full refund within the first 30 days
Reserve a place

Not ready? Join the waitlist instead.

Questions

Does the CRA apply to me?

If you place installable software on the EU market commercially, most likely yes. Pure SaaS and non-commercial open source are treated differently. PatchClock is not legal advice; for edge cases, ask a lawyer.

Do you file reports for me?

No. We prepare the drafts and track the deadlines. You review and submit through the official channel.

Do you need access to my code?

The free check only reads public files. The full product asks for read-only access to your repository, to read your lock files (or composer.json and package.json when a release has none). It never writes to it.